
Product guidance
What Is Synthetic Identity Fraud?
Learn what synthetic identity fraud is, how fabricated identities are assembled, and how platform registration signals support modern risk assessment workflows.
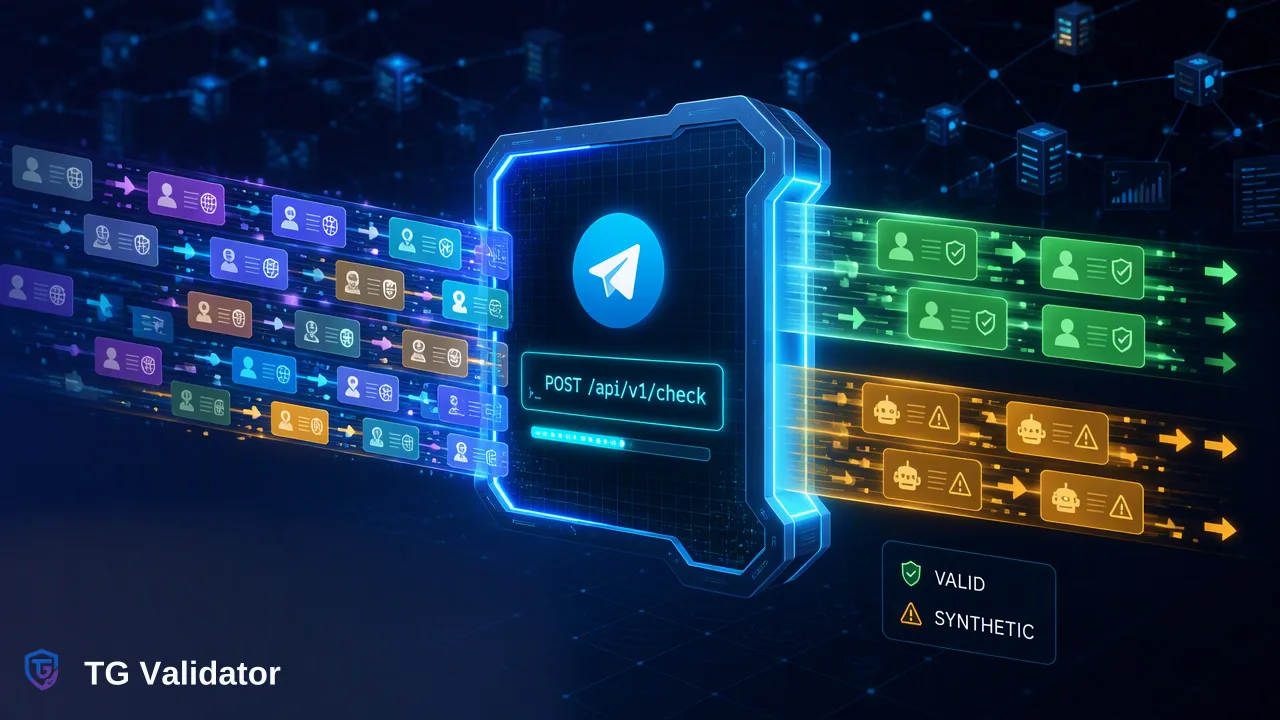
Understand the mechanics of synthetic identity fraud, how fabricated profiles are assembled, and how technical teams use platform registration signals to support risk assessment workflows.
Synthetic identity fraud occurs when bad actors combine real and fabricated data to construct a new, non-existent identity. Unlike traditional identity theft, which compromises an entire existing profile, this method blends legitimate information—such as a stolen Social Security number—with fake details to bypass automated systems. Organizations mitigate this risk by analyzing various data points, including platform registration status. A registration check provides a synchronous indicator of whether a phone number is reachable on a specific service at the time of the check, serving as one input alongside other checks in a broader risk assessment strategy.
What Is Synthetic Identity Fraud?
Synthetic identity fraud is a form of financial crime where perpetrators combine real information with fabricated data to create a completely new, non-existent identity. Traditional identity theft involves taking over a real person's established accounts or using their complete profile to open new ones. In contrast, synthetic fraud relies on constructing a hybrid profile. Organizations face significant challenges when evaluating these hybrid profiles because the legitimate components of the identity often pass basic automated checks. When a system queries a specific data point, the response may appear valid, masking the fabricated elements attached to it. Technical teams and risk operators must therefore rely on multiple distinct signals to evaluate the legitimacy of identifiers provided during onboarding or account management. Understanding the mechanics of this fabrication is the first step in designing workflows that can flag suspicious profiles for further review.
How Fabricated Identities Are Assembled
The construction of a synthetic identity typically begins with the acquisition of a legitimate, often stolen, data point. Perpetrators frequently target identifiers that have limited existing credit histories or digital footprints, such as a Social Security number belonging to a minor. Once a foundational piece of real data is obtained, bad actors blend it with fabricated information, such as a fictitious name, a newly created email address, or a recently acquired phone number. This blended profile is then systematically introduced into digital ecosystems. The goal is to build a profile that appears legitimate to automated systems and risk models. By applying for services, creating accounts, or interacting with digital platforms, the fabricated identity slowly accumulates a footprint. Over time, this footprint can make the synthetic identity look like a genuine user to organizations evaluating new applications. Instead, organizations must analyze the individual components of the identity—such as the phone number or email address—to determine if their behavior and reachability align with expected baseline patterns.
The Role of Verification Signals
To evaluate the risk associated with newly submitted profiles, organizations use various verification signals to assess the individual identifiers attached to an account. One such signal is a platform registration check, which determines whether a specific phone number is currently associated with a digital platform. When a technical team queries a number, the resulting data informs the organization whether that identifier has a presence on that specific messaging service. This provides context for risk operators reviewing the profile. However, it is critical to understand the boundaries of these signals. Instead, the registration status serves strictly as a technical indicator of reachability, adding one objective data point to the broader evaluation process.
Integrating Platform Checks into Risk Workflows
Technical teams integrate platform registration checks as one component of a multi-layered risk assessment strategy. Because synthetic identities are designed to pass isolated checks, organizations route records through multiple evaluation steps, using reachability signals to inform internal decisions and prioritize manual reviews. When implementing these checks, developers typically utilize a synchronous REST API to query identifiers during the onboarding or review phase. For example, using a platform like TG Validator, a system submits a phone number in E.164 format via a POST /api/v1/check request. The request includes an X-API-Key header and a JSON payload specifying the service type, such as {"service_type": "tg", "identifier": "<E.164 number>"}. The API processes the request synchronously, returning a response envelope containing a code, a message, and a data object. If the check is completed, the data.registered field provides a boolean value indicating the Telegram registration status. A check that cannot be decided returns a non-zero business code rather than a completed result. By incorporating this same-response workflow, organizations can programmatically flag profiles that exhibit unusual reachability patterns. If a submitted phone number lacks the expected digital footprint, the system can route the application for step-up verification or manual due diligence. This structured routing supports the review process without treating the signal as autonomous fraud detection or definitive proof of identity.
FAQ
How does a platform registration signal help in risk assessment?
A platform registration signal helps teams review profiles by adding a technical indicator of reachability to the evaluation process. When assessing potentially fabricated identities, knowing whether a submitted phone number has a presence on a specific platform can inform internal decisions, support the prioritization of manual reviews, and serve as one input alongside other checks in a multi-layered risk strategy.
How do technical teams implement synchronous registration checks?
Technical teams typically integrate registration checks using a synchronous REST API. Systems submit a phone number in E.164 format and receive a same-response result. For instance, a request might use a POST /api/v1/check endpoint with an X-API-Key header and a service_type=tg payload. The resulting data.registered boolean value is then used to route records or trigger step-up verification workflows.